

Data
Snowflake
Roiva books the Snowflake spend behind each AI initiative, Cortex AI by service type, and feeds figures from your own tables into its formulas.
What it answers
What the Snowflake work behind an AI initiative costs, and what the figures already in your warehouse say it's worth
What Roiva reads
Credits, query counts and run times from ACCOUNT_USAGE, and daily spend by usage type, Cortex AI included. Never a query's text or who ran it.
Setup
A setup script you run in a worksheet, which makes a small warehouse, a read-only role and a service user's token
What you can measure with Snowflake
Cortex AI spend
Snowflake reports Cortex AI by service type, and each is a line of its own. Map the ones an initiative uses to it and they're booked there, month by month.
Figures from your own tables
A versioned SQL query turns figures already in your warehouse, claims handled or loans underwritten, into monthly readings a formula can price, instead of numbers typed in by hand.
Credits and query load
Credits used, query counts and run times against their baseline, for an initiative that adds or moves warehouse work.
snowflake.compute.credits_used
snowflake.query.count
snowflake.query.avg_execution_seconds
Booked once
A Snowflake bill in your books is left to this connection in the months it books, so the same spend isn't counted twice. Marketplace purchases, which its usage report leaves out, still book from the bill.
A worked month
A support assistant built on Cortex
Warehouse cost, booked from Snowflake's usage by service type, for September
| AI_SERVICES, mapped to the support initiative | $2,340 | Snowflake |
| AI_INFERENCE, mapped to the same initiative | $410 | Snowflake |
$2,340 + $410
$2,750 booked to the support initiative for September
The warehouse compute behind your dashboards isn't mapped, so it stays out. Snowflake reports usage for the whole account, not per query, so a mapped service type books all of that type's spend.
Illustrative figures. Roiva keeps every input with the entry it calculates, and none of it counts until it's approved.
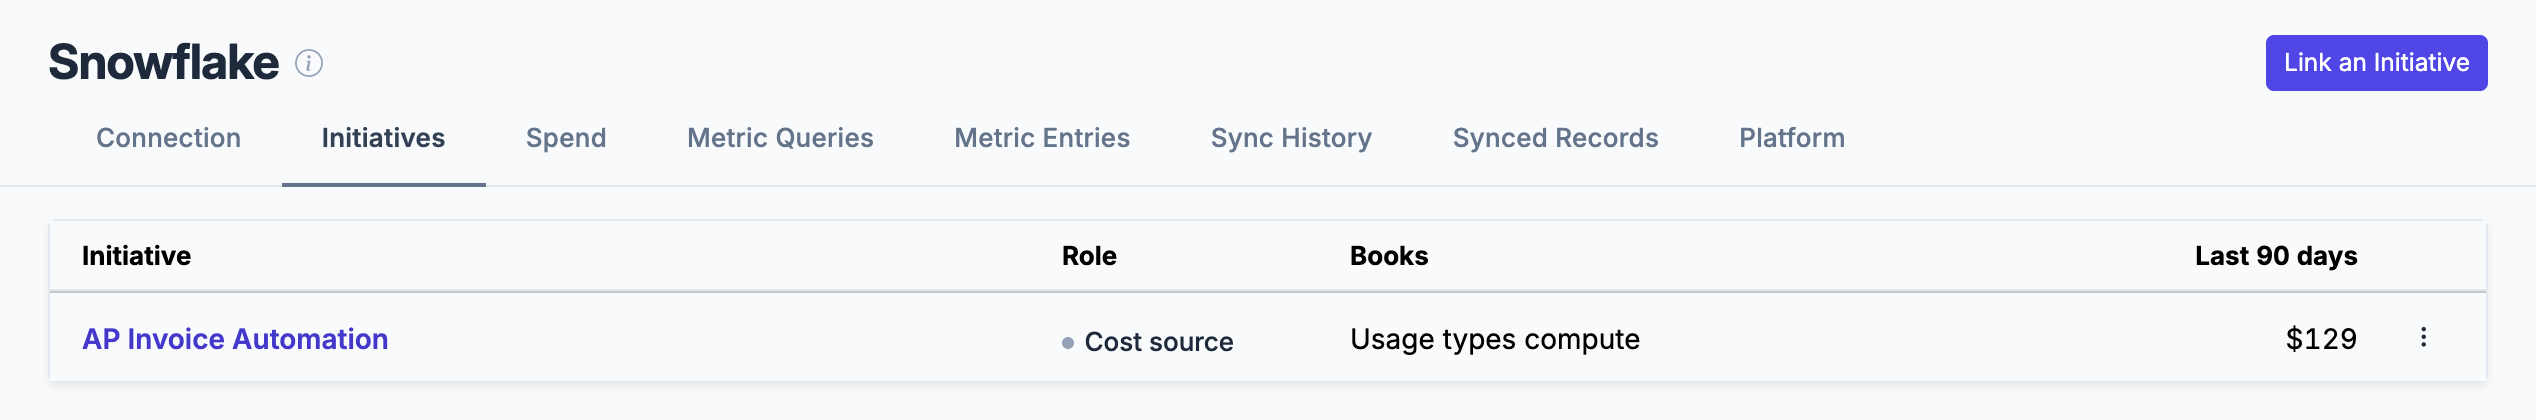
Each initiative linked to Snowflake, the usage type it books, and what it booked over the last 90 days.
What gets synced
Roiva writes these metric observations on each sync. Reference the key in a value formula to use this data in your ROI calculations.
Compute Credits
snowflake.compute.credits_used
Credits Used
count
Query Statistics
snowflake.query.count
Query Count
count
snowflake.query.avg_execution_seconds
Avg Execution Time (seconds)
duration
What Roiva keeps
Reads: Credits used, query counts and average run times from the ACCOUNT_USAGE views, added up by month inside Snowflake, and daily spend by usage type (Cortex AI by service type) from ORGANIZATION_USAGE, for the last 12 months. Never a query's text or who ran it. Your own tables only through the metric queries you write, and from those only the period, value, entity and sample_size columns, one row per month.
Keeps: Records of daily spend by usage type, with Cortex AI by service type, plus the totals worked out from them. For each metric query you write, every version of its text and the rows each version returned: a month, a number, a record count, and a breakdown's value, which is whatever the query selects as its entity. These stay after the connection is deleted, because the figures computed from them point to them.
How to connect
You connect Snowflake from inside Roiva, so you need a Roiva workspace first. Sign in to connect it now. New to Roiva? Start free with your work email, take the free assessment and create your workspace at the end, or request an invite.
- In Snowflake: Open a SQL worksheet, paste the setup script below, select all of it, and run it. Run executes only the statement under the cursor unless the whole script is selected. The script creates a small warehouse, a role that can read ACCOUNT_USAGE, a service user, an authentication policy that lets the user's token work without an IP allowlist, and the token itself
- In Snowflake: Copy token_secret from the last result. Snowflake shows it only once; to issue another later, run just the script's last statement under a new token name
- Back in Roiva: Enter your Account Identifier (SELECT CURRENT_ORGANIZATION_NAME() || '-' || CURRENT_ACCOUNT_NAME() returns it), leave Warehouse blank since the script makes ROIVA_WH the user's default, paste the token into API Key / Secret, and click Create Connection
- Back in Roiva: The connection page checks each step with the token and shows the SQL for anything still missing. Once it's all ticked, click Test Connection, then link this connection to an initiative on the Initiatives tab
- In Snowflake: To feed metrics from your own tables, create a view for each in ROIVA_METRICS.PUBLIC, which the script lets Roiva's role read and nothing else. Then in Roiva, set Metrics Schema to ROIVA_METRICS.PUBLIC in this connection's settings, and add a query for each metric on its Metric Queries tab
-- Run in a Snowflake SQL worksheet: select all of it, then click Run.
USE ROLE ACCOUNTADMIN;

-- A small warehouse for Roiva's queries; it suspends after a minute idle.
CREATE WAREHOUSE IF NOT EXISTS ROIVA_WH
  WAREHOUSE_SIZE = XSMALL AUTO_SUSPEND = 60 AUTO_RESUME = TRUE INITIALLY_SUSPENDED = TRUE;

-- The role Roiva's token is restricted to: it reads ACCOUNT_USAGE and uses the warehouse.
CREATE ROLE IF NOT EXISTS ROIVA_READER;
GRANT IMPORTED PRIVILEGES ON DATABASE SNOWFLAKE TO ROLE ROIVA_READER;
GRANT USAGE ON WAREHOUSE ROIVA_WH TO ROLE ROIVA_READER;

-- The service user Roiva signs in as.
CREATE USER IF NOT EXISTS ROIVA_SERVICE
  TYPE = SERVICE DEFAULT_ROLE = ROIVA_READER DEFAULT_WAREHOUSE = ROIVA_WH;
GRANT ROLE ROIVA_READER TO USER ROIVA_SERVICE;

-- Lets the user's token work from any address; to allow only certain
-- addresses, apply a network policy to the user instead. Authentication
-- policies live in a schema, so this one gets a database of its own.
CREATE DATABASE IF NOT EXISTS ROIVA_ADMIN;
CREATE AUTHENTICATION POLICY IF NOT EXISTS ROIVA_ADMIN.PUBLIC.ROIVA_PAT_POLICY
  AUTHENTICATION_METHODS = ('PROGRAMMATIC_ACCESS_TOKEN')
  PAT_POLICY = (NETWORK_POLICY_EVALUATION = ENFORCED_NOT_REQUIRED);
ALTER USER ROIVA_SERVICE SET AUTHENTICATION POLICY ROIVA_ADMIN.PUBLIC.ROIVA_PAT_POLICY;

-- Where your metric views live: Roiva's role may read the views in this
-- schema and nothing else. A view runs with its owner's rights, so the
-- role needs no grant on the tables behind it.
CREATE DATABASE IF NOT EXISTS ROIVA_METRICS;
GRANT USAGE ON DATABASE ROIVA_METRICS TO ROLE ROIVA_READER;
GRANT USAGE ON SCHEMA ROIVA_METRICS.PUBLIC TO ROLE ROIVA_READER;
GRANT SELECT ON ALL VIEWS IN SCHEMA ROIVA_METRICS.PUBLIC TO ROLE ROIVA_READER;
GRANT SELECT ON FUTURE VIEWS IN SCHEMA ROIVA_METRICS.PUBLIC TO ROLE ROIVA_READER;

-- The token Roiva uses. Copy token_secret from this result: Snowflake shows it only once.
ALTER USER ROIVA_SERVICE ADD PROGRAMMATIC ACCESS TOKEN ROIVA_TOKEN
  ROLE_RESTRICTION = 'ROIVA_READER' DAYS_TO_EXPIRY = 365;
Need help?
Email hello@roiva.ai with what you're seeing, and you'll hear back within one business day.
Snowflake
Start free, then connect Snowflake once your workspace is set up. Or begin with the free AI ROI exposure assessment.
Start free → Sign in to connectRelated integrations
